- Outdated infrastructure is leaving essential services exposed to increasingly sophisticated cyberattacks, Microsoft CEO Satya Nadella warns
- Unpatchable firmware creates security weaknesses that conventional updates cannot easily eliminate
- AI is accelerating vulnerability discovery, giving attackers less time to exploit weaknesses
Microsoft CEO Satya Nadella has warned that weaknesses in essential infrastructure could contribute to further disruptions as cyber threats become increasingly sophisticated.
Many connected systems rely on outdated firmware and equipment that cannot receive conventional security updates, leaving potential vulnerabilities difficult to eliminate.
The growing use of artificial intelligence in cyberattacks could make these weaknesses more dangerous for organizations responsible for essential services.
Aging infrastructure leaves critical systems exposed to cyber threats
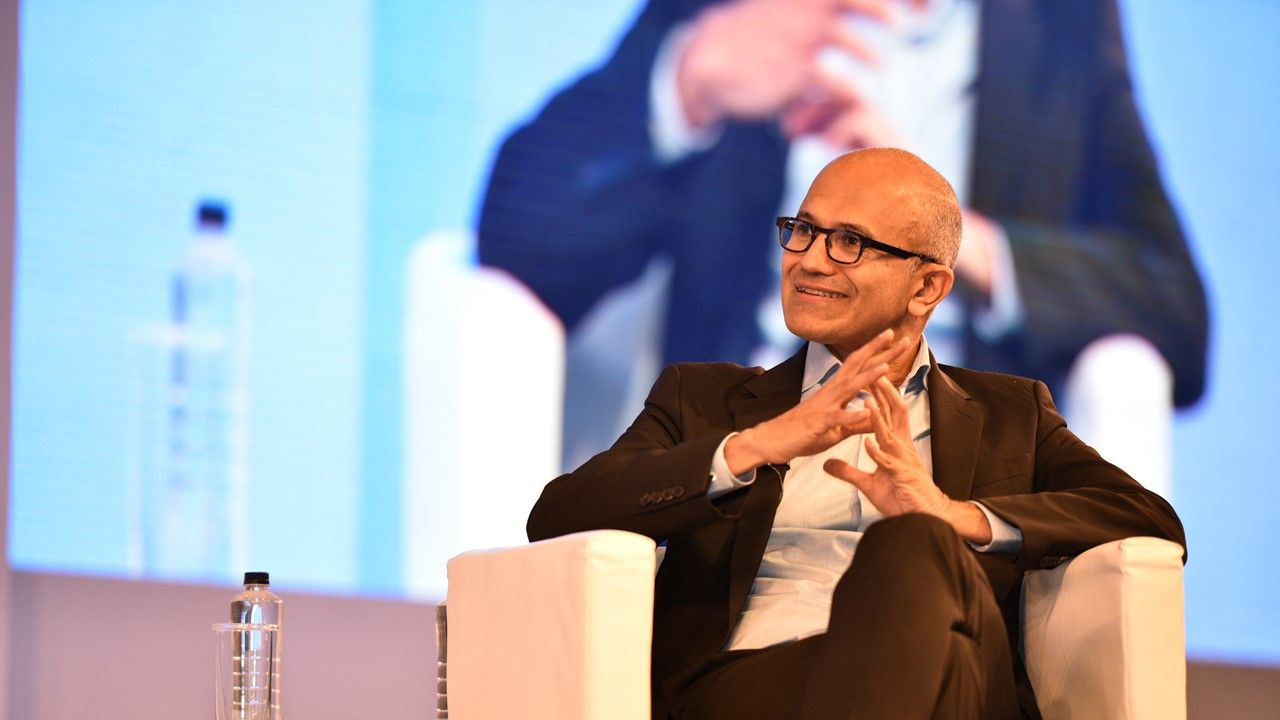
Speaking at the recent The New York Times' DealBook Summit, Nadella discussed security problems affecting equipment used across essential infrastructure.
Internet connectivity has introduced security concerns into devices originally designed to perform relatively straightforward industrial functions.
This is leaving many devices that were once considered safe increasingly vulnerable to different forms of cyberattacks.
“Remember, there is a lot of stuff in our critical infrastructure that’s unpatchable,” Nadella said.
“I mean, think about all the firmware and the chillers and the HVAC systems everywhere else. So all of that, by the way, they’re on the internet.”
Many such components now communicate through internet connections, creating additional opportunities for vulnerabilities to affect interconnected infrastructure.
Also, in recent transportation networks, certain equipment reportedly contains firmware that cannot easily receive security updates.
Modernizing these systems will require organizations to understand existing weaknesses and determine how attackers might exploit them.
The warning comes amid several significant service disruptions involving Microsoft Outlook, the National Security Agency, the Federal Aviation Administration, and Apple.
Although concerns about possible cyberattacks emerged following some incidents, officials denied that certain disruptions resulted from malicious activity.
“We put out an incident response, and we’re going to obviously take all of the learnings, both upstream architectural, as well as operational, and fix that,” Nadella said.
AI is accelerating vulnerability exploitation and security pressures
Another concern involves the increasing speed at which security vulnerabilities can be discovered and exploited.
AI tools can now easily identify software weaknesses, potentially reducing the time available for organizations to prepare defenses.
Attackers can now exploit newly discovered weaknesses quickly, forcing organizations to install available patches with considerably less preparation.
“The patch needs to go instantly from being available to being patched in production, because it’s being exploited in the wild, right? So that’s going to create instability,” Nadella added.
This creates competing security pressures because delaying updates can leave systems exposed, while rushing deployments can introduce additional operational problems.
Organizations must therefore balance immediate protection against the possibility that insufficiently tested updates could disrupt existing services.
Companies would need better malware removal tools, stronger vulnerability detection capacity and improved methods for responding to emerging threats.
They must also assess infrastructure weaknesses and develop defenses capable of operating during active security incidents.
The challenge is particularly significant for infrastructure containing older equipment that cannot accommodate conventional software updates.
Via Techcrunch